Architecting Production-Ready B2B Software With Zero Technical Debt
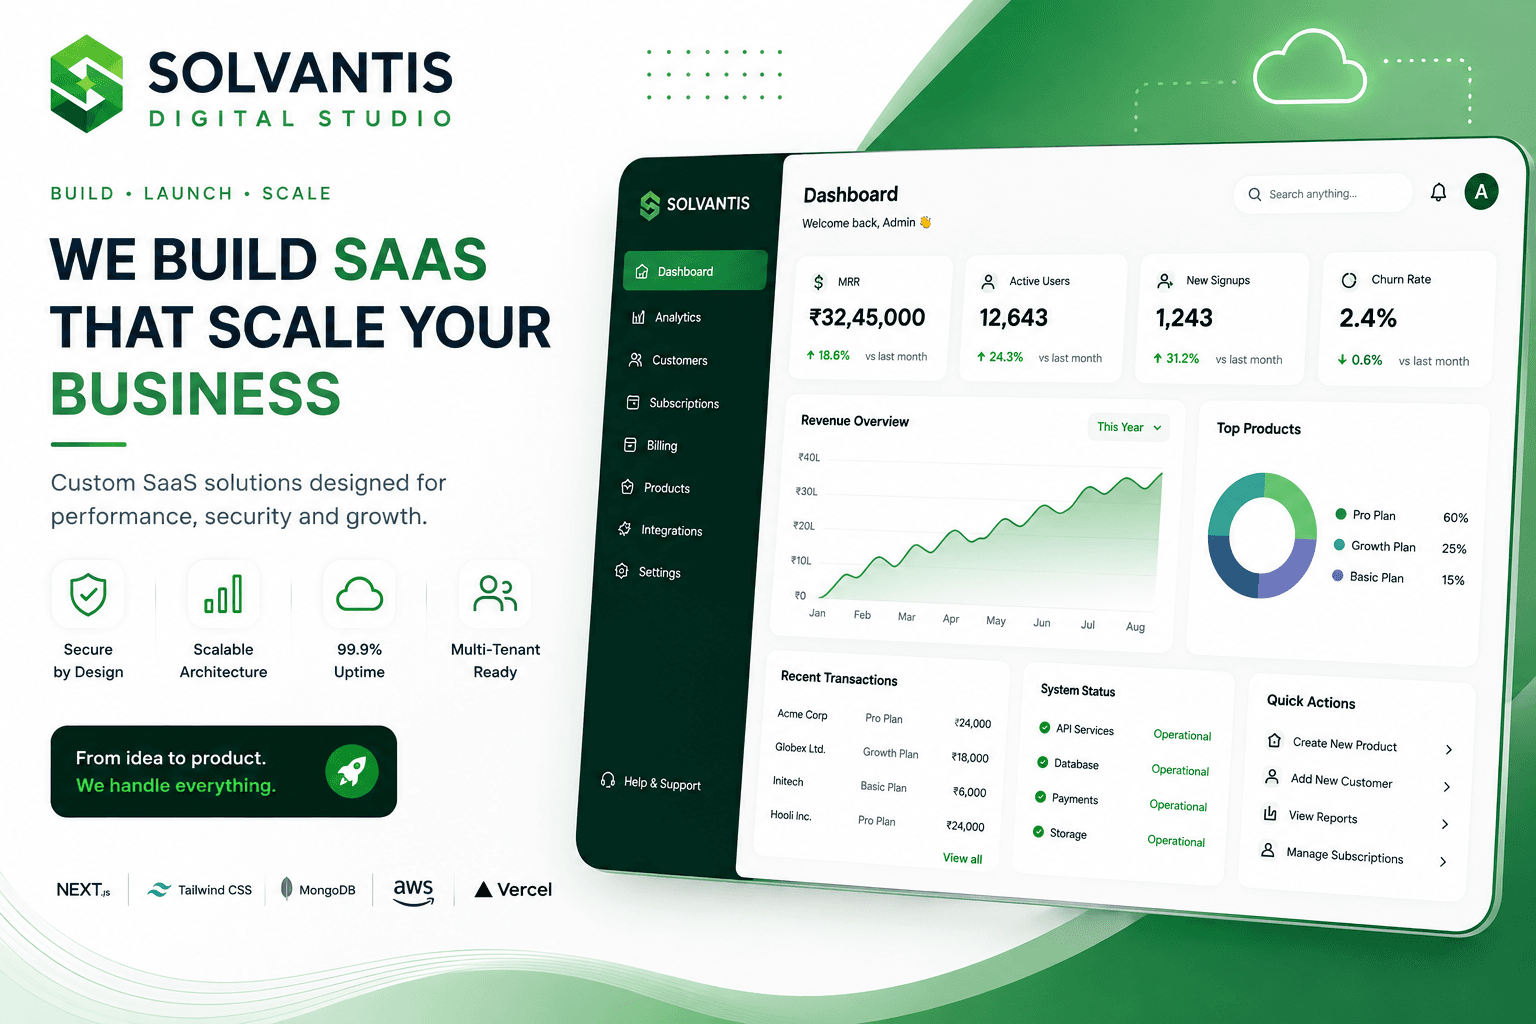
Transitioning a software concept from prototype to an enterprise-grade B2B SaaS application requires uncompromising architectural rigor. Fragile database schemas, insecure tenant scoping, and unhandled webhook edge cases frequently stall early-stage platforms during customer scaling. At Solvantis, we engineer full-stack SaaS applications built on resilient foundations: PostgreSQL Row-Level Security, automated Stripe recurring billing webhooks, granular RBAC permissions, and sub-80ms edge API response times.
Our engineering team constructs modular systems where frontend dashboards execute in React 19 with zero hydration drift, while backend serverless handlers process high-concurrency database queries through connection pooling and Redis caching. We eliminate common SaaS bottlenecks — such as failed subscription dunning, cross-tenant data leaks, and sluggish table pagination — before your first enterprise pilot commences.
Whether bootstrapping a focused vertical micro-SaaS or engineering an enterprise-scale workflow automation platform with SAML/SSO authentication, our production blueprints ensure your product is secure, auditable, and prepared to scale seamlessly from 10 to 100,000 active organizations.
Database row-level security policies enforcing zero tenant bleed.
Sub-80ms edge API response times with connection pooling.
Stripe webhook retry reliability with automated dunning.
Granular audit trails and OWASP Top-10 defense compliance.
Explore B2B SaaS Foundation Modules
Inspect architecture modules engineered specifically for multi-tenant data isolation, enterprise authentication, and automated subscription billing.
Isolated Customer Organization Boundaries & Scoping
Enterprise SaaS customers demand rigorous data segregation. We enforce cryptographic tenant isolation at both the API gateway and database layer using PostgreSQL Row-Level Security (RLS) and schema scoping. Every database query is automatically scoped to the verified organization context, eliminating cross-tenant data leakage risks.
// Tenant-Scoped Database Query Layer
export async function getTenantWorkspace(tenantId: string) {
  return await db.transaction(async (tx) => {
    await tx.execute(sql`SET LOCAL app.current_tenant_id = ${tenantId}`);
    return await tx.query.workspaces.findFirst({
      where: eq(workspaces.organizationId, tenantId)
    });
  });
}Architectural Standards for Enterprise Scale
Every B2B SaaS platform we engineer adheres to rigorous isolation, scalability, and security benchmarks.
Isolated Tenant Architecture
Strict organization-scoped data boundaries using PostgreSQL Row-Level Security (RLS), preventing cross-tenant leakage.
Resilient Subscription Webhooks
Stripe & Razorpay recurring billing pipelines with automated seat provisioning, prorated upgrades, and dunning sequences.
Granular RBAC & Team Controls
Self-serve team invites, SAML/SSO enterprise authentication, and fine-grained role permissions with complete audit trails.
High-Concurrency Next.js 15
Edge-rendered React 19 dashboards with sub-80ms API response times and zero visual layout shifts under heavy concurrent load.